Nothing on the page can break it
- Available now
Shadow DOM isolation: no page selector reaches inside, so jQuery, Bootstrap and Inertia page transitions stay outside.
- Available now
Livewire: wire:model, server re-renders and wire:navigate keep the text and the caret, tested in three browser engines.
Comfortable with Japanese IME
- Coming in v1.0
Composition is respected — confirming a conversion never fires a stray Enter.
One composer require
- Available now
Server-side HTML sanitising on save and on output, with no Node.js on your side.
- Available now
Image uploads to Laravel storage, checked and re-encoded on the server.
Try it
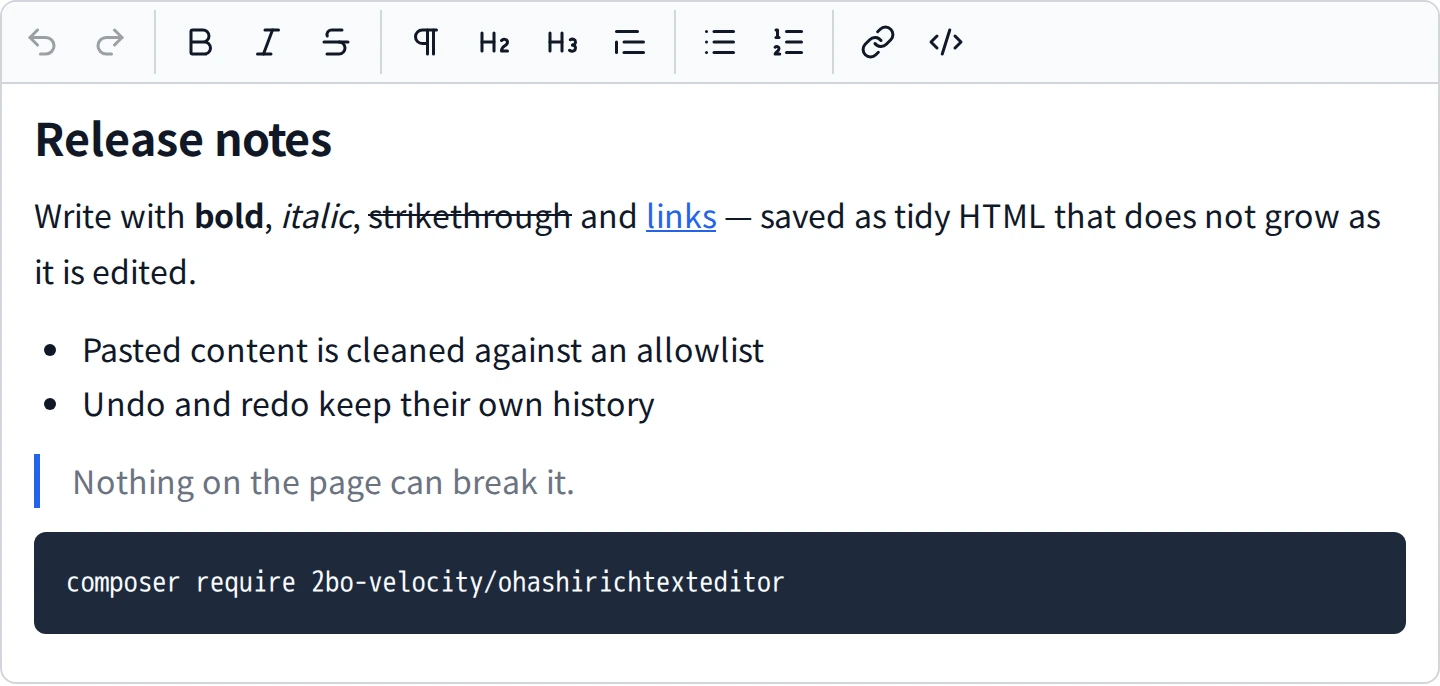
Today's build: formatting, lists, links, code blocks, undo and clean paste. Image uploads need a server, so this static demo leaves them out.
Load unsafe HTML
Stored content is cleaned before the editor shows it. Load this into the editor above and see what is left.
<p onclick="steal()">Hello <span style="color:red">world</span></p>
<img src="x" onerror="alert('XSS')" alt="photo">
<script>alert('XSS')</script>
<a href="javascript:alert('XSS')">click me</a>
<x-tracker>hidden</x-tracker>
What the editor kept
Press the button to see the result.
From install to safe output
Requires PHP 8.4+ and, for the Laravel integration, Laravel 12 or 13.
1Install
composer require 2bo-velocity/ohashirichtexteditorphp artisan vendor:publish --tag=ohashi-editor-assets2Put the editor in a form
<script type="module" src="{{ asset('vendor/ohashi-editor/ohashi-editor.js') }}"></script><x-ohashi-editor name="body" :value="old('body', $post->body)" />3Sanitise on save
use OhashiEditor\Laravel\Casts\SanitizedHtml;protected function casts(): array{return ['body' => SanitizedHtml::class]; // sanitised on save}4Display safely
{{-- sanitised again on output --}}<x-ohashi-content :html="$post->body" class="prose" />
Security you can check
- The server is the trust boundary: HTML is sanitised on save and again on output.
- Built on symfony/html-sanitizer with PHP 8.4's native HTML5 parser — it reads HTML the way browsers do.
- One allowlist shared by the browser and the server, and one set of test cases run in Chromium, Firefox, WebKit and PHP.
- Works under a strict Content-Security-Policy: no inline scripts or styles.
License
AGPL-3.0-or-later
Free for open-source projects and any project whose full source you can publish under the AGPL.
Commercial license
For closed-source products, SaaS and client work that cannot take on the AGPL's source-disclosure obligation.
support@2bo-velocity.com